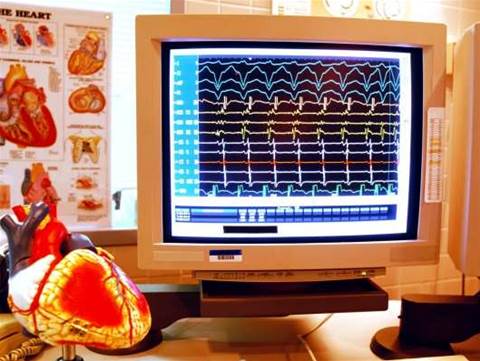
The group was able to connect to devices, obtain patient information and cause them to shut down.
"Our investigation shows that an implantable cardioverter defibrillator is potentially susceptible to malicious attacks that violate the privacy of patient information and medical telemetry," the researchers wrote.
"The devices may experience malicious alteration to the integrity of information or state, including patient data and therapy settings for when and how shocks are administered.
"When these systems include wireless computing devices, additional precautions are necessary to ensure that the computing devices appropriately balance safety with convenience and do not introduce unacceptable risks."
The researchers recommended that device manufacturers implement basic systems that can alert patients and require authentication for a connection without consuming too much power.
Researchers hack into pacemakers
Got a news tip for our journalists? Share it with us anonymously here.
Add techpartner.news as your trusted source
Partner Content

Rise of the frontier partner: Why the channel model is being rewritten

Building higher tier service offerings with cost-effective, proactive monitoring

Promoted Content
Kris Manché, Panel Expert at Index Brisbane

Cisco’s AI Rally Kit delivers high performance AI without the engineering pain

Access to more: what Crayon becoming SoftwareOne means for partners